A machine
Second-stage implant, editor extensions, tasks that run on folder open, build configs, fake fonts, persistence, credentials. Check a machine
Last updated:


Download it for macOS, Linux or Windows, verify it, and run it. It asks what
you need, one question at a time, and changes nothing until you type yes.
./polinridergit log showed nothing.A script on the infected machine reads your last commit’s timestamp, winds the system clock back to it, amends that commit with the payload, restores the clock, and force-pushes. What lands is a commit with an ordinary date and your name on it.
Detection has to be content scanning of every ref, reconciled against push events. Nobody does that by eye across fifty repositories.
A machine
Second-stage implant, editor extensions, tasks that run on folder open, build configs, fake fonts, persistence, credentials. Check a machine
A GitHub account
Every repository, every branch and tag, read against GitHub’s push record. Restores branches where the evidence survived. Clean an account
An organization
The same check across every repository an org owns, then one repository at a time or one fix for all of them. Clean an organization
Every future push
A scanner you copy into your own repository. No third-party action, nothing leaves your infrastructure. Set up CI
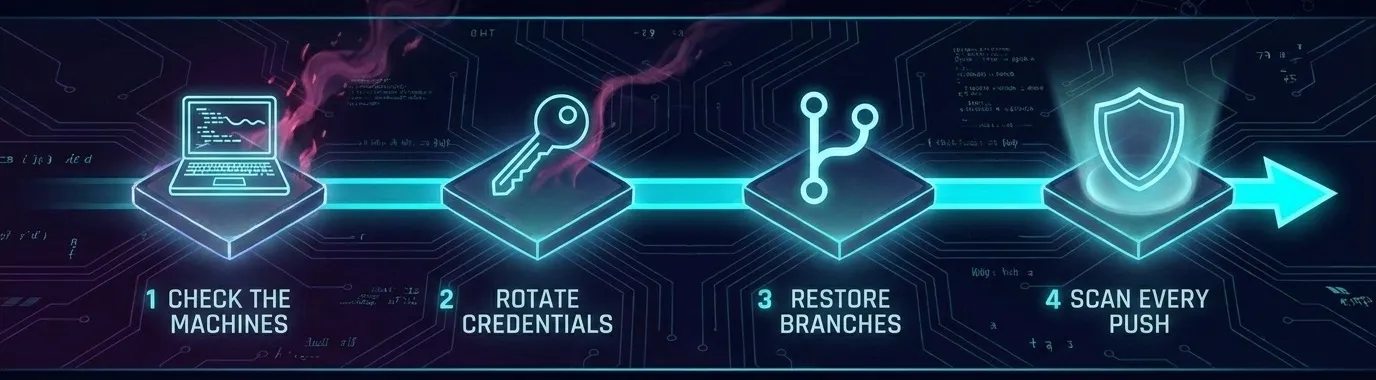
Cleaning GitHub while an infected machine still holds a valid token undoes the work within minutes. Why the order is fixed
A tool you run during an incident should be honest about its limits.
clean cuts it out in
place and keeps the infected original in quarantine. On GitHub, each fix
shows what it would change and pushes only when you type yes.You are being asked to run unknown code on a machine you may believe is compromised. That deserves evidence rather than a promise.
| Built during a real incident | 57 repositories and 304 refs on the author’s own account. Two of ten restore points turned out to be infected themselves |
| Indicators reviewed weekly | Every review logged, including the weeks nothing changed |
| Every commit signed | The direct counter to the campaign’s own backdated-amend technique |
| Releases carry provenance | A sigstore attestation proves each binary came from this repository’s CI |
| It scans itself | CI fails if the repository matches its own indicators once its detection code is excluded |